Disclosure
EscapeSafeBrowser — online examination mode
Researcher: Mohammad Fadi Alfandi (0xiZO)
Reported to: Jordan University of Science and Technology — Cybersecurity Department
Acknowledged: 20 January 2026
I identified a security vulnerability in the EscapeSafeBrowser mode used by online examination platforms and reported it responsibly to the university’s Cybersecurity Department. The department acknowledged the report and issued the letter of appreciation below.
This page intentionally contains only a high-level summary. Technical details, student data, and any information that could help misuse the platform are withheld. No student data is included here.
Evidence
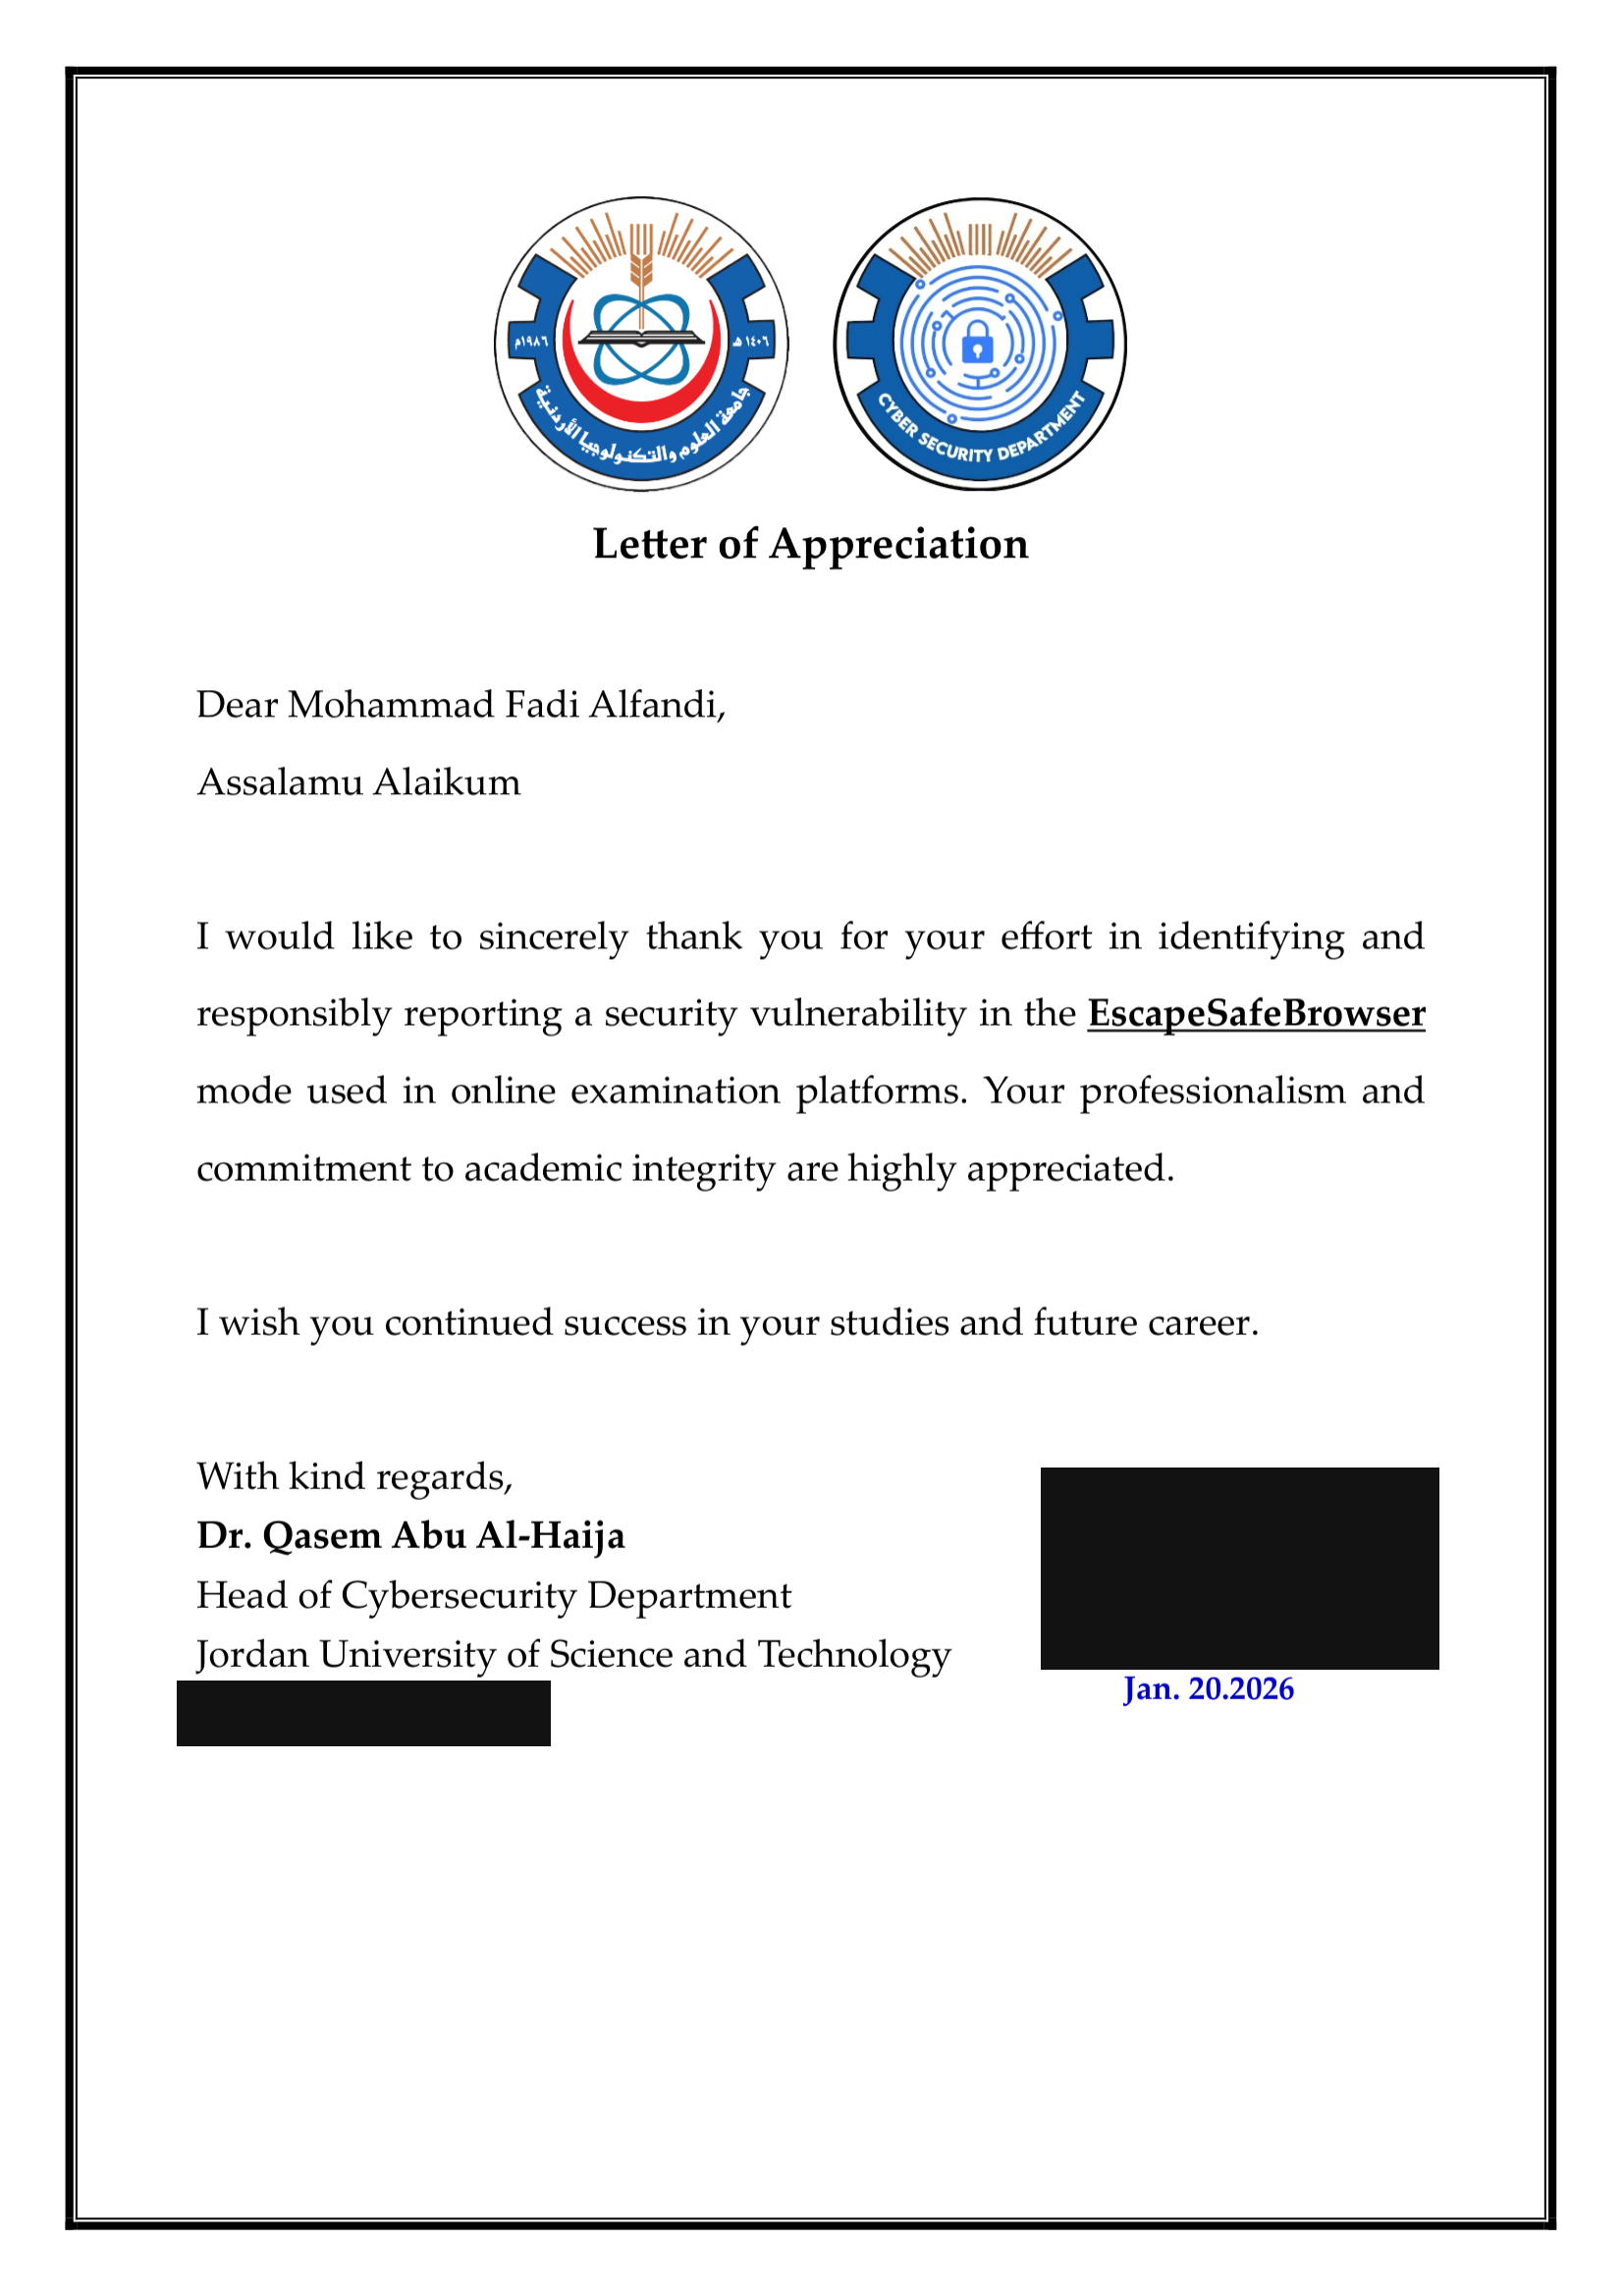
The signer’s signature and personal email address have been redacted for privacy. The original letter is available to verifiers on request.
Scope
This disclosure relates to the university’s online examination platform. I reported the issue to the university’s Cybersecurity Department and have not published exploit steps or student data. My broader security work is limited to systems I own, CTF environments under their published rules, and targets for which I have explicit authorization.
Identity
- Name: Mohammad Fadi Alfandi
- Handle: 0xiZO
- GitHub: hackeringtrue
- Site: hackeringtrue.github.io